Nexuvius

Verify every

Identity and access security tools you run yourself, built on open standards.

We start at the root of trust, the identity provider, and build outward: the gateway that enforces it and the tools that audit it. Every product carries a Tamil name, a nod to where Nexuvius comes from.

One request, start to finishSimulated
  1. Maya, on her work laptopopens the team wiki
  2. ஆதி
    Aadhiproves who it is
    Signed in
  3. அரண்
    Aranchecks every request
    Allowed
  4. Your apps and APIsanswer only what got through
    200 OK

Built on open standards

  • OpenID Connect
  • OAuth 2.0
  • SAML 2.0
  • Passkeys (WebAuthn)
  • DPoP
  • PAR
  • SCIM 2.0
  • Shared Signals (CAEP, RISC)
  • Token Exchange
  • Mutual TLS
  • SARIF

Aadhi has passed the OpenID Foundation's Basic OP conformance tests in our own run. Formal certification is in progress.

The products

What we're building

Three products work today and two more are planned. Aadhi came first and runs our own sign-in. Pick one to see what it does.

ஆதி

Aadhi Tamil for "origin"

A self-hosted identity provider for your apps and AI agents. One small server and a database, on infrastructure you control.

  • Passkeys, authenticator apps and recovery codes
  • Single sign-on with OpenID Connect and SAML 2.0
  • Scoped, revocable tokens for AI agents acting for a person
  • Separate organizations for each of your customers
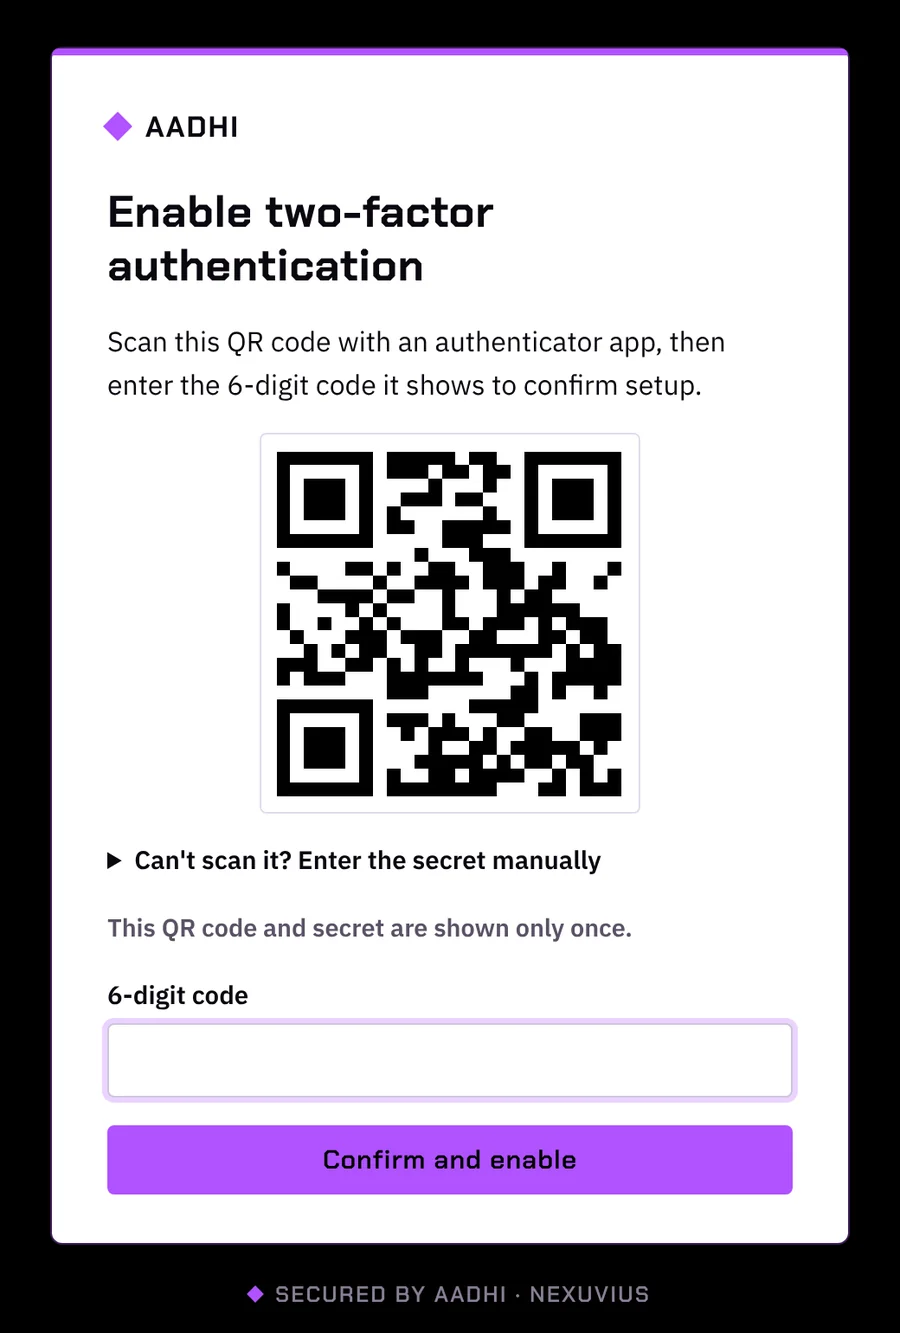
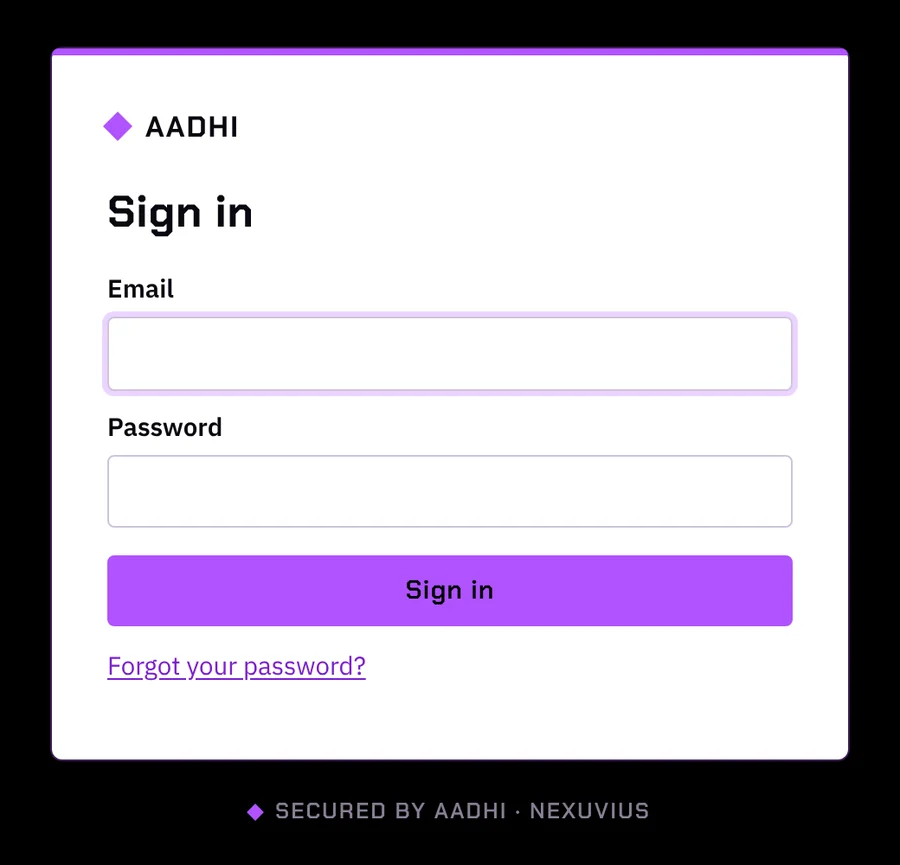
Working build, running live
Aadhi page for turning on two-factor authentication with a QR code
Aadhi sign-in page
அரண்

Aran Tamil for "fortress"

A Zero Trust gateway that sits in front of your internal apps. It checks who is asking, what they may reach and the state of their device, on every request.

  • Sign-in through Aadhi or any OpenID Connect provider
  • Deny by default, with policy you can change while it runs
  • Device checks: operating system, disk encryption, screen lock
  • Ends a session the moment the identity provider revokes it
Working build
Try it: change the requestSimulated
Signed in
Group
Asks for
Disk encrypted
Screen lock
  1. IdentitySigned in through Aadhi
  2. Policyengineering may open /deploy
  3. DeviceEncrypted, screen lock on
  4. Your appForwarded over mutual TLS
Allowedaudit: allow user=maya@example.com groups=[engineering] path=/deploy

Example policy: engineering may open everything and needs an encrypted disk and a screen lock. Guests may open /wiki/public only.

விழி

Vizhi Tamil for "eye"

An auditor for AWS access policies. It finds access that is wider than it should be and explains each finding in plain English, with the fix.

  • 23 kinds of policy, from IAM and S3 to KMS and Lambda
  • Catches public access, privilege escalation and confused-deputy risks
  • Reports as Markdown, PDF, JSON or SARIF for code scanning
  • Shows what changed since the last scan
Working build
vizhi
Sample output with made-up policy names.
  • காவல்

    Kaval Planned

    "Guard". Security monitoring and detection, built to take in the audit trails the other products produce.

  • நெறி

    Neri Planned

    "The right path". A compliance engine that maps security controls to the evidence that proves them.

How we build

Three rules we hold ourselves to

  • Standards firstOpenID Connect, OAuth, and the RFCs around them, implemented as written so our tools work with yours.
  • Yours to runOur tools run on your own servers, so your users' data stays with you. Standard protocols mean you are never locked in.
  • Proven, not promisedWe back claims with evidence you can check, like Aadhi passing the OpenID Foundation's Basic OP conformance tests, and a security review before every release.

See it working, not just described

Nexuvius Notes is a small demo app that signs you in with Aadhi, so you can try passkeys and two-factor sign-in from the app's side. Or write to us and we will show you around.